
What Is ISO 27001?
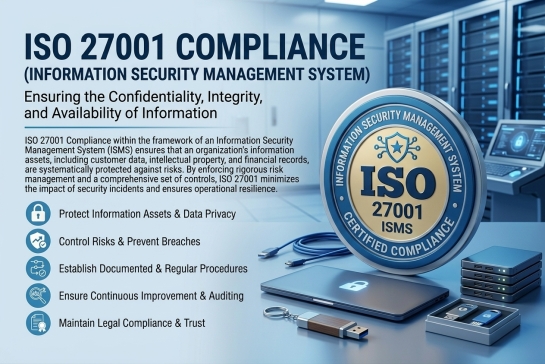
ISO 27001 is a well-known international standard for Information Security Management Systems (ISMS), developed by the International Organization for Standardization (ISO) and the International Electrotechnical Commission (IEC).
This standard provides a systematic framework for organizations to identify, manage, protect, and continually improve their information assets. ISO 27001 covers all major aspects of information security, including data protection, access control, cyber risk management, security incident management, incident response, and business continuity.
The latest version of the standard, ISO/IEC 27001:2022, introduced significant changes compared with the previous version, including:
• Revising and restructuring the information security controls;
• Adding new controls in areas such as Cloud Security, Threat Intelligence, Data Masking, and Secure Coding;
• Greater emphasis on managing information security risks in the supply chain.
This version replaced ISO/IEC 27001:2013 and is considered the most comprehensive update of the standard in recent years.
ISO 27001 is applicable to any organization that deals with information; in fact, almost all organizations today deal with valuable information. This standard can be implemented according to the size, type of activity, and complexity of the organization’s information security environment.
This standard is applicable to organizations such as:
• IT and software companies;
• Financial institutions and banks;
• Healthcare and medical organizations;
• Government agencies;
• Professional service companies;
• Manufacturing and industrial organizations with sensitive information.
As the world’s most widely used information security management standard, ISO 27001 is increasingly becoming an important requirement in customer contracts, legal requirements, tenders, and supplier qualification in the global supply chain.
ISO 27001 provides organizations with a systematic framework to identify, manage, protect, and continually improve their information assets.
As the world’s most widely used information security management standard, ISO 27001 is increasingly becoming an important requirement in customer contracts, legal requirements, tenders, and supplier qualification in the global supply chain.